rewrite this content and keep HTML tags as is. This is content from rss feed and I don’t need their *Daily Debrief Newsletter*, their tags from bottom like this *Share this articleCategoriesTags*, Editorial Process section, phrases like *Featured image from Peakpx, chart from Tradingview.com*, SPECIAL OFFERS and similar sections – just remove such sections and save only article itself:
In brief
Microsoft said attackers compromised a Mistral AI software download used by developers.
The malware allegedly stole credentials and could damage some Linux systems.
Mistral said it has no evidence that its infrastructure was compromised.
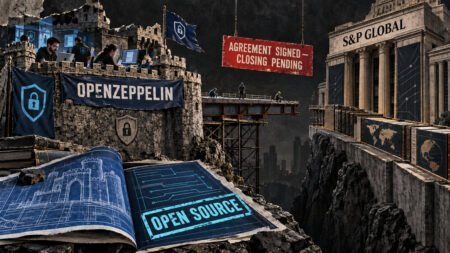
Microsoft Threat Intelligence said Monday that attackers inserted malicious code into a Mistral AI software package distributed through PyPI, a popular platform developers use to download Python software tools.
In a post on X, Microsoft said the malicious code automatically ran when developers used the software on Linux systems. The code downloaded a second malicious file called transformers.pyz from a remote server and launched it in the background.
“The file name transformers.pyz appears deliberately chosen to mimic the widely used Hugging Face Transformers library and blend into ML/dev environments,” Microsoft wrote.
The company said the malware primarily worked as a credential stealer capable of collecting developer login information and access tokens. Microsoft also said the malware avoided Russian-language systems and included code that could randomly delete files on some systems that appeared to be located in Israel or Iran.
Reports link the latest attack to the broader “Shai-Hulud” malware campaign that began in September and targets software supply chains by infecting trusted developer packages and stealing credentials from compromised systems.
“Shai-Hulud, that spoopy Git worm thingy everyone’s been yapping about, has been open-sourced,” cybersecurity firm VX Underground wrote on X. “What does this mean? TeamPCP, or someone else, has released the fully weaponized worm for you.”
Microsoft advised organizations to isolate affected Linux systems, block the associated internet address, search for signs of infection, and replace potentially exposed credentials.
On Tuesday, Mistral said on its website that it was impacted by a supply-chain attack tied to the broader TanStack security incident. The company said an automated worm associated with the attack led to compromised NPM and PyPI package versions being published.
“Current investigation indicates that an affected developer device was involved,” the company wrote. “We have no indication that Mistral infrastructure was compromised.”
Node Package Manager or NPM is one of the world’s largest software download platforms for JavaScript developers. It has increasingly become a target in crypto-related cyberattacks because many blockchain apps, wallets, and trading platforms rely on software distributed through the service. In September, Ledger CTO Charles Guillemet warned that hackers had compromised widely used NPM packages in an attack that could redirect crypto transactions and steal funds.
“The affected packages have already been downloaded over 1 billion times, meaning the entire JavaScript ecosystem may be at risk,” Guillemet wrote on X at the time.
Other recent attacks used poisoned NPM packages tied to fake crypto trading bots and blockchain tools to spread malware through Ethereum smart contracts.
Daily Debrief Newsletter
Start every day with the top news stories right now, plus original features, a podcast, videos and more.